 Cloud Agent Lab
Private by default
The S3 bucket blocks all public access. A bucket policy lets exactly one CloudFront distribution read the files, so the only way in is through the CDN.
CSCE 412 · Project 5
This page is stored in a private Amazon S3 bucket, delivered over HTTPS by Amazon CloudFront, and reached through a custom domain on Route 53. The project's goal is a team of specialized AI agents that plans, deploys and verifies this infrastructure, with a person approving every consequential change.
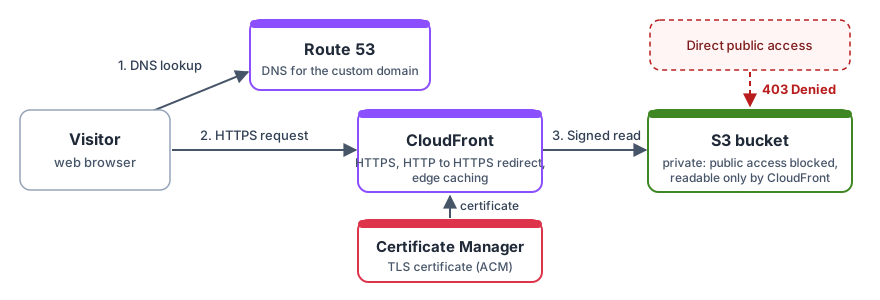
The S3 bucket blocks all public access. A bucket policy lets exactly one CloudFront distribution read the files, so the only way in is through the CDN.
A certificate from AWS Certificate Manager covers the domain and its www name. CloudFront redirects plain HTTP to HTTPS before serving anything.
An agent saying "the site is secure" is not evidence. Checks record real status codes, certificate details and response headers so every claim can be confirmed.
403 Access Denied.Want proof? The Security page can inspect the real response headers of this site from your browser.